
Cyberattacks are becoming more sophisticated as businesses move applications, customer data, APIs, and infrastructure into interconnected digital environments. A single unpatched vulnerability can potentially expose sensitive information or disrupt critical services. This is where security testing becomes an important part of modern software and infrastructure management.
Penetration Testing is a controlled security assessment in which ethical hackers simulate realistic attacks against an authorized application, network, server, or infrastructure. The objective is not to damage a system but to discover weaknesses before malicious attackers can exploit them.
For beginners, understanding the phases of penetration testing is an excellent starting point for learning ethical hacking, vulnerability assessment, network security, and application security.
This guide explains the major phases, testing methodologies, a practical lab scenario, career opportunities, challenges, and how emerging technologies are changing cybersecurity.
Table of Contents
What Is Penetration Testing?
Penetration testing, commonly called pentesting, is an authorized security assessment designed to identify vulnerabilities by simulating attack techniques.
Security professionals may examine areas such as:
- Web applications
- APIs
- Networks
- Servers
- Cloud infrastructure
- Mobile applications
- Authentication mechanisms
- Databases
- Internal corporate systems
The ultimate objective is to answer an important question:
“Could an attacker successfully compromise this environment, and what should the organization do about it?”
Unlike a simple vulnerability scan, a professional assessment attempts to understand whether discovered weaknesses can actually be combined or exploited within the defined scope.
Why Is Penetration Testing Important?
Organizations increasingly depend on digital platforms for business operations, payments, communication, and customer services. As part of digital transformation, the number of applications and interconnected systems continues to grow.
This expansion also increases the potential attack surface.
Regular security assessments can help organizations:
- Identify exploitable vulnerabilities
- Validate existing security controls
- Detect configuration weaknesses
- Assess authentication and authorization controls
- Reduce security risks
- Protect sensitive information
- Improve incident preparedness
- Support compliance requirements
- Prioritize remediation efforts
Penetration Testing vs Vulnerability Scanning
These terms are related but not identical.
Vulnerability scanning primarily focuses on discovering known weaknesses through automated or semi-automated tools.
Penetration testing goes further by evaluating whether weaknesses can be meaningfully exploited within an authorized environment and by assessing the potential business impact.
For example, a scanner may identify an outdated service. A pentester may investigate whether that weakness creates a realistic path toward unauthorized access—without exceeding the agreed scope.
Core Phases of Penetration Testing
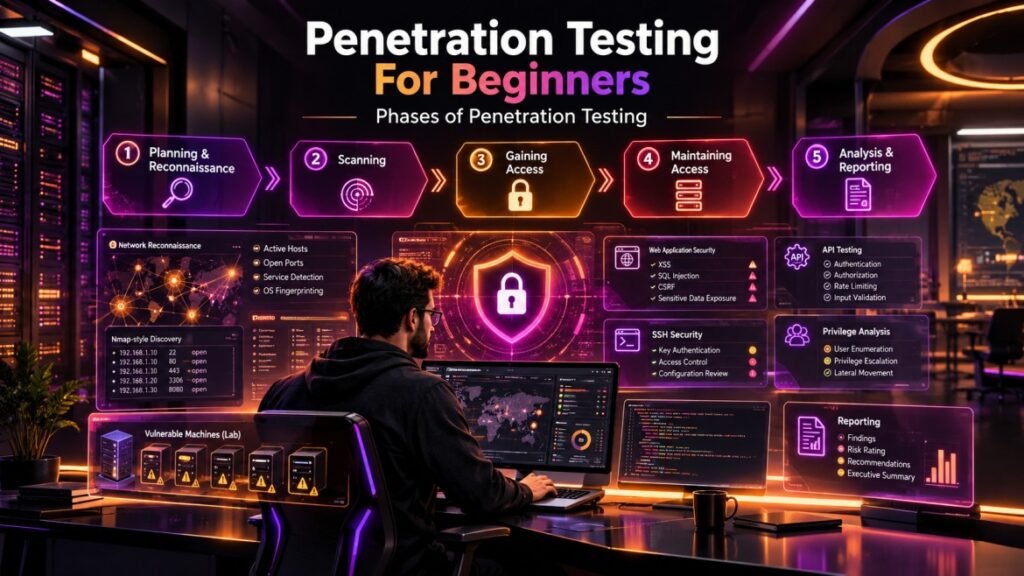
A structured security assessment generally follows several stages. Different organizations and frameworks may name or combine these stages differently, but the underlying process remains similar.
1. Planning and Reconnaissance
Planning is the foundation of a successful security assessment.
Before any technical testing begins, the tester and organization establish the rules of engagement.
Important planning considerations
The team typically defines:
- Target systems
- Testing objectives
- Scope and exclusions
- Testing window
- Authorized techniques
- Communication channels
- Emergency contacts
- Data-handling requirements
- Reporting expectations
Reconnaissance then focuses on gathering information about the authorized target.
Information may include:
- Domains and subdomains
- IP addresses
- Technologies
- Publicly exposed services
- Application architecture
- Potential entry points
Reconnaissance can be passive or active depending on the engagement rules.
Example: A security team assessing a company’s web application may first map its approved domains, application components, technologies, and externally visible services.
2. Scanning
After reconnaissance, testers analyze how the authorized environment responds to different requests and interactions.
Scanning can involve both automated tools and manual investigation.
Static and dynamic approaches
Static analysis examines information without necessarily interacting deeply with the running target.
Dynamic analysis evaluates the behavior of a running application or service.
The objective is to identify potential weaknesses such as:
- Unexpected open services
- Misconfigured systems
- Weak security controls
- Outdated components
- Authentication issues
- Potential application vulnerabilities
Scanning results should not automatically be treated as confirmed vulnerabilities. Security professionals validate findings to reduce false positives.
3. Gaining Access
This phase evaluates whether identified weaknesses can be exploited under the approved rules of engagement.
Depending on the environment, testers may assess vulnerabilities involving:
- Authentication
- Authorization
- Input validation
- SQL injection
- Cross-site scripting
- Misconfigured services
- Weak credentials
- Insecure configurations
The goal is to determine the realistic security impact rather than simply collect a list of vulnerabilities.
Example
Suppose an authorized training application contains an input-validation weakness. A tester may demonstrate, within the lab environment, how the weakness could allow unintended application behavior.
The tester then documents the vulnerability, evidence, risk level, and recommended remediation.
4. Maintaining Access
In controlled assessments, maintaining access is used to determine whether an attacker could retain access after an initial compromise.
This phase can simulate characteristics of sophisticated threats, including advanced persistent threats.
However, persistence techniques should only be tested where they are explicitly authorized.
Security teams may instead focus on questions such as:
- Could compromised credentials be reused?
- Can an attacker move between systems?
- Are privileged accounts adequately protected?
- Would monitoring detect suspicious activity?
- Can security controls terminate unauthorized sessions?
The purpose is to understand how far an attacker could potentially progress and how effectively defenders could detect and contain the activity.
5. Analysis and Reporting
Reporting is one of the most valuable parts of a professional security assessment.
A good report converts technical observations into actionable business information.
A typical report may include:
- Executive summary
- Assessment scope
- Methodology
- Findings
- Severity ratings
- Technical evidence
- Potential business impact
- Affected assets
- Remediation recommendations
- Risk prioritization
- Retesting requirements
A strong report should be understandable to both technical teams and business stakeholders.
For example:
Technical finding: Weak authentication control.
Business impact: Unauthorized users may potentially gain access to sensitive account information.
Recommendation: Strengthen authentication controls, enforce appropriate password policies, implement multi-factor authentication where applicable, and monitor suspicious login activity.
Testing Methodologies
Not every security assessment follows the same information model. The amount of information provided to testers can significantly change the approach.
Open Box Testing
In an Open Box assessment, the tester receives extensive information about the environment.
This may include:
- Application architecture
- Source-code information
- Network diagrams
- Credentials for authorized test accounts
- Infrastructure documentation
Advantages
- Deeper assessment
- Better coverage
- Faster identification of complex weaknesses
- Useful for development and internal security reviews
Closed Box Testing
Closed Box testing, sometimes called Single Blind testing, provides limited internal information.
The approach attempts to simulate an external attacker who has little knowledge of the organization’s internal environment.
It can help evaluate:
- External attack surface
- Public-facing applications
- Perimeter security
- Information exposure
- Detection capabilities
Covert or Double-Blind Testing
In a Double-Blind or covert assessment, the security and IT teams may not be fully informed about the exercise.
This approach can test not only technical defenses but also an organization’s detection and incident-response capabilities.
Because unexpected testing can create operational risks, strong authorization and carefully defined rules are essential.
External vs Internal Penetration Testing
Another important distinction is whether testing focuses on external or internal infrastructure.
External Testing
External assessments concentrate on systems accessible from outside the organization.
Examples include:
- Public websites
- Internet-facing APIs
- Remote access services
- External infrastructure
- Public cloud endpoints
Internal Testing
Internal assessments examine security controls from within an organization’s environment.
They may evaluate:
- Internal networks
- Employee-accessible systems
- Network segmentation
- Privilege management
- Internal applications
- Lateral movement risks
Using both approaches can provide a more complete view of an organization’s security posture.
Practical Demonstration: Vulnerable Machine Lab
Beginner cybersecurity courses often use deliberately vulnerable machines to demonstrate the pentesting lifecycle in a safe environment.
One example is a Death Note vulnerable machine, where learners can observe how reconnaissance, enumeration, exploitation, and privilege escalation fit together.
Important: Such exercises should only be performed against intentionally vulnerable machines or systems for which you have explicit authorization.
Reconnaissance
The demonstration begins by identifying the lab machine and examining its exposed services.
Tools such as Nmap and netdiscover can be used in an isolated training environment to understand network visibility and identify potential attack surfaces.
The learning objective is to understand how an attacker builds an initial picture of a target.
Enumeration
After identifying exposed services, the next step is to investigate them more deeply.
A lab exercise may involve:
- Discovering directories
- Examining publicly exposed files
- Reviewing
robots.txt - Identifying application technologies
- Looking for intentionally planted clues
Directory enumeration and similar activities help learners understand why unnecessary information exposure can become a security risk.
Exploitation
The vulnerable machine demonstration may then show how a deliberately weak authentication mechanism can be abused to obtain access.
For example, the lab uses Hydra to demonstrate a controlled brute-force scenario against an intentionally vulnerable SSH service.
The important lesson is not the command itself but the underlying security weakness:
Weak credentials + exposed authentication service = increased attack risk.
Organizations can reduce this risk through strong authentication policies, MFA where appropriate, rate limiting, account lockouts, monitoring, and secure configuration.
Privilege Escalation
Obtaining an initial foothold does not necessarily mean an attacker has complete control.
Privilege escalation examines whether a low-privileged account can gain higher-level permissions because of configuration mistakes, excessive privileges, insecure files, or other weaknesses.
In the Death Note lab demonstration, intentionally hidden information and SSH configuration weaknesses are used to illustrate the concept of moving from limited access toward root-level control.
For beginners, this stage demonstrates an important cybersecurity principle:
Security is not only about preventing initial access; it is also about limiting what an attacker can do after access is obtained.
Common Tools Beginners Can Learn
A beginner-friendly cybersecurity learning path can gradually introduce tools such as:
- Nmap — network discovery and service enumeration
- Wireshark — network traffic analysis
- Burp Suite — web application security testing
- OWASP ZAP — web application security testing
- Metasploit Framework — security testing and exploitation research
- Gobuster — content and directory discovery
- Hydra — authentication security testing in authorized labs
- Nessus — vulnerability assessment
- Nikto — web server security assessment
Tools are only one part of the profession. Understanding networking, operating systems, authentication, HTTP, databases, programming, and security principles is more important than memorizing commands.
Challenges in Penetration Testing
Security professionals face several challenges when conducting assessments.
1. Rapidly Changing Technology
Cloud platforms, APIs, containers, serverless architectures, and AI-based applications constantly change the attack surface.
2. False Positives
Automated scanners can produce findings that require manual validation.
3. Limited Testing Windows
Organizations may allow only short maintenance windows, making prioritization essential.
4. Business-Critical Systems
Aggressive testing can potentially disrupt production systems. Professional testers therefore carefully follow rules of engagement.
5. Evolving Attack Techniques
Attackers continuously develop new techniques, requiring security professionals to keep learning.
6. Reporting Complexity
Finding a vulnerability is only part of the job. Explaining its business impact and providing useful remediation guidance is equally important.
Future of Penetration Testing
The future of technology will significantly influence cybersecurity testing.
As organizations adopt cloud computing, artificial intelligence, IoT, APIs, automation, and distributed applications, security assessments will increasingly need to cover complex environments.
AI-Assisted Security Testing
Artificial intelligence can help security professionals:
- Analyze large volumes of security data
- Identify suspicious patterns
- Prioritize vulnerabilities
- Assist with reconnaissance
- Generate testing hypotheses
- Improve security reporting
However, AI-generated findings still require human validation.
Continuous Security Testing
Traditional security assessments may occur periodically. Modern organizations are increasingly moving toward continuous security validation integrated with development and operations.
Security testing can become part of:
Development → Testing → Deployment → Monitoring → Remediation → Retesting
Cloud and API Security
Cloud infrastructure and APIs are becoming central to modern applications. Future security professionals will need strong knowledge of:
- Cloud identity and access management
- API authentication
- Container security
- Infrastructure as Code
- Secrets management
- Cloud configuration
- Supply-chain security
Opportunities for Beginners
Cybersecurity offers multiple career paths for people who develop strong technical foundations.
Potential roles include:
- Junior Penetration Tester
- Security Analyst
- Vulnerability Analyst
- Application Security Tester
- SOC Analyst
- Security Engineer
- Red Team Analyst
- Cloud Security Engineer
- API Security Tester
Beginners should focus on fundamentals before chasing advanced tools.
Recommended Learning Path
Step 1: Learn networking fundamentals.
Step 2: Understand Linux and Windows administration.
Step 3: Learn HTTP, DNS, TCP/IP, and common network protocols.
Step 4: Study web application security.
Step 5: Learn scripting with Python, Bash, or PowerShell.
Step 6: Practice only in authorized labs.
Step 7: Study recognized security frameworks and methodologies.
Step 8: Build a portfolio using legal CTFs and vulnerable training environments.
Step 9: Learn how to write professional security reports.
Step 10: Develop communication and risk-analysis skills.
Certifications That Can Help
Certifications are not a replacement for practical knowledge, but they can provide structured learning.
Beginners may explore certifications and learning paths related to:
- CompTIA Security+
- eJPT
- PNPT
- OSCP
- Web application security certifications
- Cloud security certifications
The right certification depends on experience, career objectives, budget, and technical background.
The Impact of IT on Modern Cybersecurity
The impact of it—particularly the rapid expansion of software, cloud infrastructure, APIs, and connected systems—has transformed cybersecurity from an isolated IT function into a business-critical discipline.
A modern organization may have thousands of endpoints, applications, APIs, cloud resources, and user identities.
Consequently, security cannot depend solely on a perimeter firewall.
Organizations need layered controls involving:
- Secure software development
- Identity management
- Network segmentation
- Endpoint protection
- Vulnerability management
- Security monitoring
- Incident response
- Regular security assessments
This broader security model is becoming increasingly important as digital transformation accelerates.
Best Practices for Safe Pentesting
If you are learning cybersecurity, follow these principles:
- Test only systems you own or have explicit permission to assess.
- Use intentionally vulnerable machines for practice.
- Understand the scope before testing.
- Never target random public websites.
- Avoid unauthorized credential attacks.
- Keep testing environments isolated.
- Document your activities.
- Follow responsible disclosure practices.
- Never use discovered credentials for unauthorized access.
- Treat security testing as a professional discipline rather than a shortcut to unauthorized systems.
Final Thoughts
Learning the phases of penetration testing provides beginners with a practical understanding of how security professionals approach an authorized attack simulation.
The process starts with planning and reconnaissance, moves through scanning and controlled exploitation, evaluates the possibility of maintaining access, and finally converts technical findings into actionable security recommendations.
The most important lesson is that cybersecurity is not simply about using hacking tools. It requires knowledge of networks, applications, operating systems, authentication, cloud environments, programming, risk management, and business operations.
As the future of technology brings more AI-powered applications, cloud platforms, APIs, and connected systems, skilled cybersecurity professionals will have increasingly important roles in protecting digital infrastructure.
For beginners, the best strategy is simple: learn the fundamentals, practice in legal environments, understand why vulnerabilities exist, and develop the ability to explain how organizations can fix them.